Google Hacking Database
Catalog of Google search queries, known as dorks, that surface exposed files, devices, and sensitive pages.

- Categories
- Search and Discovery
- Price
- Free
- Setup
- Easy to use
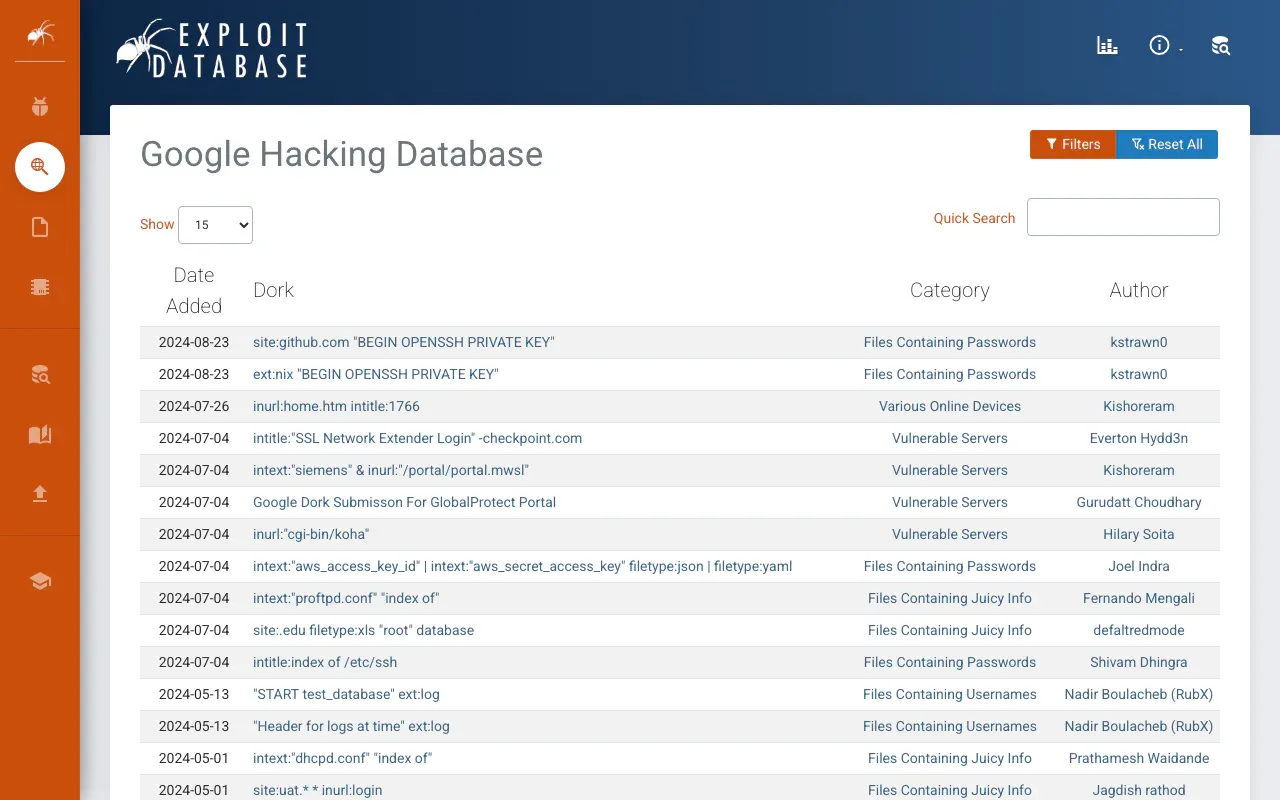
The Google Hacking Database is Offensive Security’s catalog of Google dorks: search queries that find things people did not mean to leave in public. Exposed documents, login panels, configuration files, cameras, error messages that leak paths. Each entry has a date, a category, and an author. The collection lives on Exploit-DB.
It is a reference, not a scanner. You copy a query, you adapt it to your target or your scope, you run it in a search engine, you look at what came back. Google, Bing, and others change their operators and their appetite for this kind of traffic. A dork that worked last year can return nothing today.
How I use it
When I have a domain and I want to know what a search engine already indexed. That is often faster than crawling the site yourself, and it is the indexed copy that an outsider would find. I keep a short list of dorks I actually understand (site:, filetype:, inurl:) and I use GHDB when I need a reminder of a pattern I have not run in a month.
I do not run the whole catalog against a random company for fun. A lot of these queries exist because someone found a real exposure. Replaying them without a reason is how you become the event in someone else’s log.
Why it is listed
Because “just Google it” is still half of OSINT, and this is the grown-up cheat sheet. It is free, it is categorized, and it does not require an account. I keep it for the questions, not for a finished result.