HackCheck
Searches billions of breach records by email, username, password, or other identifiers and shows which leaks contain the query.

- Categories
- Breach DataEmail OSINTUsername OSINT
- Price
- Freemium
- Setup
- Some setup
HackCheck is a breach search engine. You give it an identifier and it tells you which leaked datasets contain that value. The site currently advertises more than 16 billion records.
You are not limited to an email. Paid plans search by username, full name, hash, IP, phone number, password, and domain. That matters on a case where the email is a dead end and the reused handle or the hash is not.
Why it is a Gem
Have I Been Pwned is the right first check for “was this email in a named breach.” HackCheck is what I use when I need the deeper pile, more query types, and a result I can dump into a file without writing my own parser.
The free tier exists. The paid tiers are cheap for professional work. Silver is $4.99 for two weeks. Gold is $14.99. Diamond is $39.49 a month, or less on an annual bill. They take cards through Stripe and a list of common cryptocurrencies.
I would rather pay that than babysit a collection of combo-list sites that disappear, rate-limit, or lie about what they hold.
How a search works
You search from the dashboard. Bulk results come back as a downloadable JSON or TSV file. Bulk search takes up to 10,000 identifiers in one job.
A Breach Monitor is a separate add-on. You point it at an email, username, password, or domain and HackCheck mails you when that value shows up in a new dataset. Monitoring starts at $2 a month, or $1 a month if you pay annually.
The REST API is part of the paid plans rather than a separate product. Rate limits are tied to the plan, including IP allowlists and requests per second. If you need a custom cap, they say to ask.
Limits
A hit tells you a value appeared in a leak. It does not tell you who the person is, or whether the password still works. Treat passwords and hashes as exposure evidence. Rotate what you are authorized to rotate. Do not replay credentials.
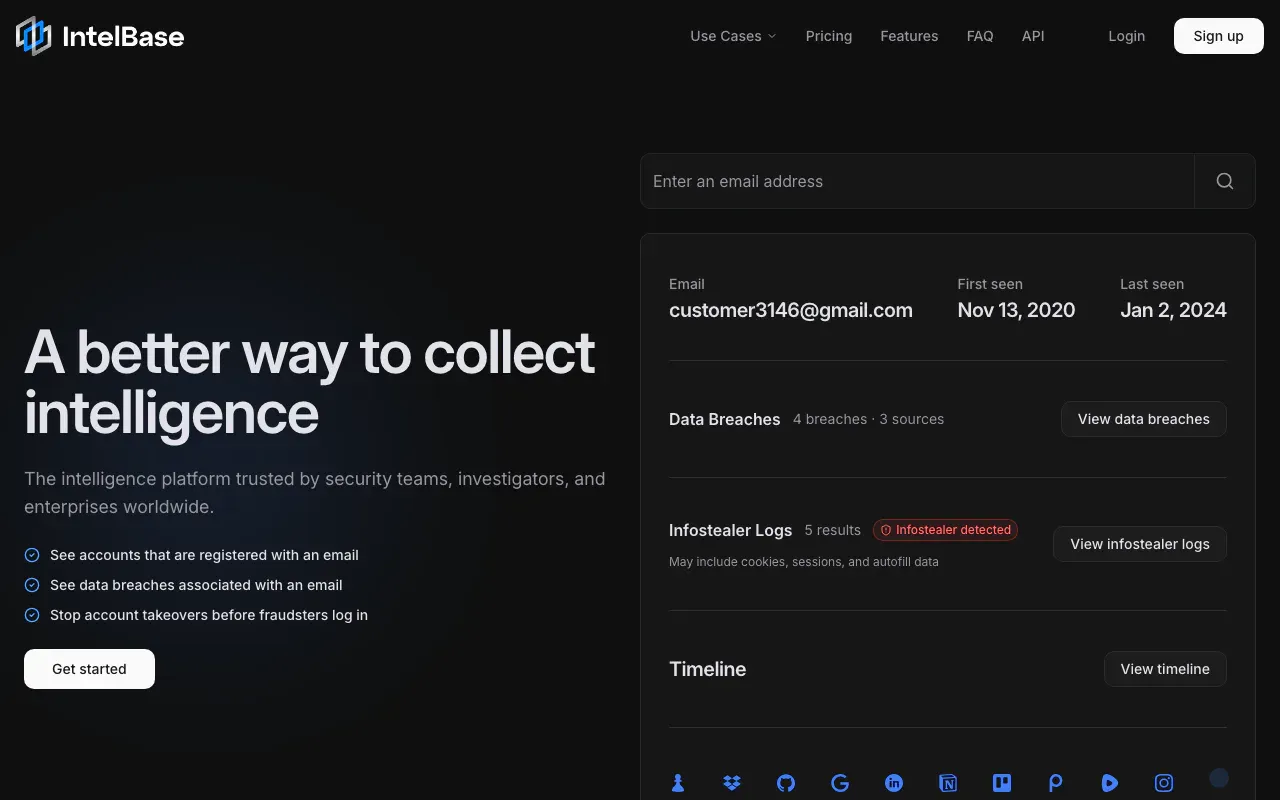
No breach engine holds every leak on earth. If HackCheck is quiet and the case still smells like a compromise, I still check IntelBase for stealer-log coverage and Have I Been Pwned for the well-documented public breaches.